Notabene Integration for Crypto Firms on Notabene Transact
On Notabene Transact, a crypto firm itself hands each withdrawal to custody at ReadyToSettle and matches each deposit to its transfer. The firm also decides flags in its case tool. Protofire builds that side of a Notabene integration. We deployed Safe on 120+ EVM networks, where it secures $2B+.
Reviewed by Luis Medeiros, Field CTO at ProtofireLast reviewed: November 2026
On this page
Work shipped for 60+ networks and 95+ protocols, including




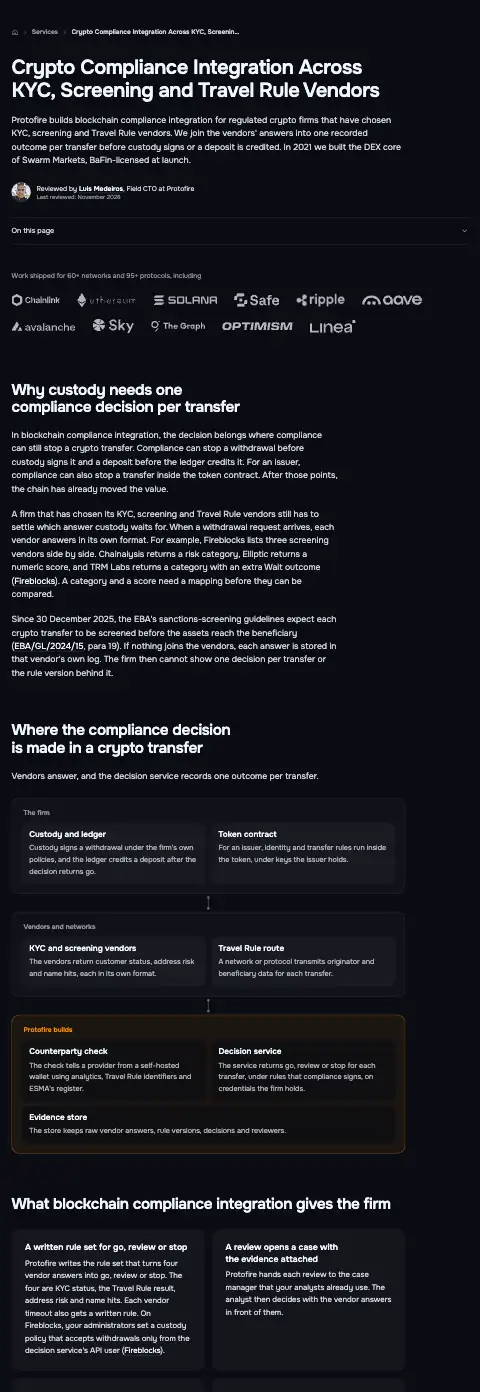
Who handles each part of a Notabene transfer
Notabene exchanges the Travel Rule data, and the funds leave from the firm's custody. The hash links the two records.
Customer screens and custody
Policies and counterparty network
Settlement gate
Webhook consumer
Deposit matcher
Flag hand-off and records
When a Notabene requirement times out, your firm decides
When a counterparty does not answer, Notabene skips the requirement, and your firm decides what happens to the money.Notabene skips it "so no transfer waits forever on a counterparty that does not answer" (Notabene). Under counterparty coordination, the wait on the sending side is "up to 1 minute by default". If your firm sends the funds anyway and records the hash, the transfer reads SettledIncompleteAuthorization until the counterparty authorizes (Notabene). On a new account the default is Flag, so transfers wait for review until someone changes that default.
One hold in Notabene does not time out. Personal data waits until the receiving institution confirms the address (Notabene). So a withdrawal sent before that confirmation leaves without its originator data. EU law asks for that data "in advance of, or simultaneously or concurrently with" the transfer (Art. 14(4)). It also says the originator's provider shall not execute a transfer "before ensuring full compliance with this Article" (Art. 14(8)). Both rules come from Regulation (EU) 2023/1113, which applies from 30 December 2024. Protofire's settlement gate therefore holds such a withdrawal unless your compliance team has signed a rule to release it.
On deposits, the deadline that your firm sets matters more. Once a CASP asks for missing information, the EBA says its deadline "should not exceed three working days for transfers taking place within the Union, and five working days for transfers received from outside of the Union" (EBA/GL/2024/11, 4 July 2024, para 56). Notabene records each skip, so your team can spot a provider that repeatedly fails to send data.
EU law also covers a provider that repeatedly fails to send data (Art. 17(2) of Regulation (EU) 2023/1113). The beneficiary's provider must then follow one of two courses. The first is to take steps, which may start with warnings and deadlines, before rejecting that provider's transfers or restricting or ending the relationship. The second is to take those measures directly. In both cases, the beneficiary's provider reports the failure to its AML supervisor.
Where the requested information is not provided by the set deadline, the CASP or ICASP should make the decision on whether to reject, return, suspend or execute the transfer in line with its risk-based policies and procedures as specified in paragraphs 52 and 53.
Notabene versions, environments, events and wallet providers
- Versions
- Notabene's v1 page recommends that new integrations start on v2.1, which is Notabene Transact. SafeTransact v1 "is scheduled for retirement in 2027" (Notabene). The v2.1 changelog gives no release date (Notabene).
- Environments
- A sandbox, plus production in the EU or the US. "Your institution lives in one region" (Notabene).
- Events
- Notabene sends four webhook events through Svix. Each event is signed with a secret that starts with whsec_ and is retried until a 2xx answer. Events arrive unordered and contain no personal data (Notabene).
- Wallet providers
- Fireblocks, Dfns, Zodia and Utila can connect Notabene on the firm's behalf (Notabene).
Checked November 2026 against Notabene's documentation.
What a Notabene integration from Protofire includes
Withdrawals handed to custody at ReadyToSettle
Your approvers see a withdrawal once its transfer reads ReadyToSettle, unless a signed rule says otherwise. Protofire's settlement gate creates the transfer under a ref, so a repeat of the same call does no harm. The gate compares the asset, amount and address with the custody request. It then records the executed hash (Notabene).
Deposits credited after their Travel Rule data arrives
A customer balance grows from a settled transfer or from a decision that your team recorded. Protofire builds the matcher that looks up each deposit and holds unmatched funds in a suspense position.
Timeouts and flags sent to your case tool
A skipped requirement or a withdrawal held on personal data becomes a case in your case tool, with the policy verdict attached. Approvals go back through force-authorize with a reason that names the analyst. Notabene's documentation also says that "your team cannot add a flag by hand" (Notabene). Protofire's service relays what an analyst decided, and it uses a credential that your firm can delete.
Ownership proof for each self-hosted address
A signed message in eip-191 or bip-322 is checked when it is submitted. A self-declaration or a screenshot keeps the status Submitted until your compliance team decides (Notabene). Protofire builds the review queue and records which method was used.
A webhook consumer that drops repeated events
Protofire's webhook consumer checks the Svix signature on each event and drops repeats by svix-id. The consumer then reads the transfer for its status.
Policies drafted and tested before the Flag default changes
Protofire drafts the policies with your compliance team and tests transfers in sandbox. A firm on a v1 integration needs a migration plan now.
Self-managed or wallet-managed Notabene connection
A custody platform can take over the wallet side of the Notabene connection.In a wallet-managed integration, Fireblocks, Dfns, Zodia or Utila "handle address registration, ownership and most webhook delivery" (Notabene). In the self-managed default, the firm handles registration, ownership and webhooks itself.
Addresses and customers
Self-managed (the default): The firm registers both, in sandbox and again in production
Wallet-managed: The wallet provider registers addresses and their ownership
Webhooks
Self-managed (the default): The firm handles each event
Wallet-managed: The provider delivers most events
Other Travel Rule providers
Self-managed (the default): The routes that the firm contracts
Wallet-managed: On Fireblocks, "Notabene cannot run alongside Sumsub or GTR. TRUST works alongside any provider." (Fireblocks)
What Protofire builds
Self-managed (the default): Registration, the webhook consumer, the settlement gate and the deposit matcher
Wallet-managed: The settlement gate, the deposit matcher, and the ledger and case links
Three cases for matching a deposit to its transfer
Deposits reach your wallet in three orders, and each order needs its own handling.The deposit matcher calls GET /api/v1/transfers/match each time the wallet sees a deposit. It retries the call within a window that the firm sets (Notabene).
Travel Rule data arrives before the funds
Notabene sends transfer.created.v3 with direction Incoming, usually before the funds are sent. The firm's policies approve or flag the transfer. When the funds arrive, the matcher links them to the transfer, and the ledger credits the customer.
Funds arrive before the Travel Rule data
The first lookups come back empty, because the sending institution records its hash once its withdrawal completes on chain. The matcher retries with back-off and adds the memo tag for XRPL or Stellar.
No Travel Rule data within the window
Notabene's docs say to "treat the deposit as having arrived without Travel Rule data, and ask your customer where the funds came from". The firm then creates the transfer itself with the hash. The firm also asks the sending institution for its data, or it records the sender that its customer declares.
Our record: Safe multisig and its two transaction hashes
A Safe gives one transfer two hashes, and Protofire's settlement gate records the executed one with Notabene.The first hash is the safeTxHash that the Safe's owners sign. The second is the ethereumTxHash of the transaction "once it's executed" (Safe). The executed hash identifies the transfer on chain, which is why the gate records that one. The same question comes up in multi-party approval on Safe, where a signed intent and an executed transaction have to be told apart.
Protofire deployed Safe on 120+ EVM networks, where it secures $2B+. The Safe Ecosystem Foundation wrote in May 2026 that Protofire "has been contributing to Safe since 2018". See our Safe multisig work.
Steps of a Notabene project with Protofire
- Step 1
An engineer reads your Notabene setup before the call
Before the call, an engineer reads your Notabene version and region. The engineer also reads which custody platform signs and where deposits wait before credit. A written proposal follows. - Step 2
Gate, matcher and consumer tested in sandbox
The settlement gate, the deposit matcher and the webhook consumer run in sandbox. Test transfers cover a flag, a skip and a deposit whose funds arrive before its data. - Step 3
Policies signed before the first live transfer
Your compliance team signs the policies and the exceptions that the settlement gate may release. - Step 4
Who owns the code and who runs the integration
The code and runbooks are yours. Each service reaches Notabene with a credential and the whsec_ webhook secret. Your staff create that credential in Notabene's dashboard, keep it in your vault and can delete it. Your team runs the integration, or Protofire operates it through managed onchain operations. Protofire's operation follows a written scope that names each write call, from transfer creation and settle to force-authorize and reject.
How work with Protofire on Notabene starts
You start by telling Protofire which Notabene version you run, which custody platform signs and where deposits wait before credit.The first proposal names each requirement that your backend answers through the API. The proposal also names the ledger entry behind each transfer status. The terms below apply to each phase, as set out on how we work.
- Proposal
- In writing, one business day after the discovery call: findings, a plan in phases and the first step we recommend.
- Price
- Fixed per phase when you commission it, against written acceptance criteria. Overruns inside them are ours to absorb, invoices follow delivered milestones, and you can stop at any phase boundary. Anything we operate after launch is priced in the proposal as its own recurring line, with the notice to end it.
- Ownership
- Code we write for you, contracts, the keys and credentials this work creates and the accounts your infrastructure runs in are yours by contract, within the license of any third-party software involved. Keys that a custody platform or a staking provider holds under its own key model stay with it under your contract; every other custody key stays with you or the custodian you appoint. Where the scope places something on servers we rent, it says what moves to you and when. An NDA is available from your first message, and we sign a data processing agreement (DPA) together with it.
- After launch
- Delivery closes with a hypercare window and a defect warranty, with their terms written into the proposal. A service we operate continues under its written scope until that scope ends.
- Access
- Read-only by default. A role that can start requests only if your written scope names one; never a signer, approver, administrator, key holder or recovery role on your contracts, wallets or custody platform. Services we build call each platform on credentials your staff issue and keep in your vault. Anything that approves or moves funds runs in your environment, and a scope under which we operate a service lists every write call it makes. Where the scope has us operate nodes, validators, monitors, explorers or indexers, it names the role and any key we hold on those servers, and in your own cloud account you can remove it.
- Licenses
- Protofire is an engineering firm and holds no financial or crypto-asset license; licensed activity stays with you and your providers.
How we work shows a worked proposal.
Four cases where Notabene or your custody platform is enough
- Your wallet provider already connects Notabene. Fireblocks, Dfns, Zodia or Utila may book each hold and credit inside its own platform. In that case, the provider's setup and Notabene's dashboard can be enough.
- Your outgoing volume is low, or you want vendor help. As of November 2026, Notabene's pricing page lists a free tier with a monthly cap on outgoing volume. That tier lets a firm "Receive and respond to unlimited incoming transactions". Notabene's paid plans list "Onboarding and implementation support, live training and SLAs" (Notabene).
- You have not chosen a Travel Rule provider yet. Start with our EU Travel Rule guide, which compares eight routes with Notabene among them.
- You need another Notabene product. This page covers Notabene Transact. SafeGateway and Notabene Flow are other Notabene products.
Protofire builds the systems around Notabene and takes no compliance decision. Your counsel decides whether a skipped requirement or a self-declaration satisfies your supervisor, and we build the rule they choose. Protofire holds no financial or crypto-asset license. Your firm keeps the keys and the policies.
Related guides and services
FAQ
What is a Notabene integration?
Who can build a Notabene integration for an exchange or a custody firm?
Does Notabene screen our customers against sanctions lists?
Can a Fireblocks workspace run Notabene next to another Travel Rule provider?
Where do Notabene and Protofire appear in our DORA register of information?
Get a proposal
Tell us what you are building. An engineer reads it, we have a short call, and the written proposal follows within one business day.