Skip to content

Crypto Compliance Integration Across KYC, Screening and Travel Rule Vendors

Protofire builds blockchain compliance integration for regulated crypto firms that have chosen KYC, screening and Travel Rule vendors. We join the vendors' answers into one recorded outcome per transfer before custody signs or a deposit is credited. In 2021 we built the DEX core of Swarm Markets, BaFin-licensed at launch.
Luis Medeiros

Reviewed by Luis Medeiros, Field CTO at ProtofireLast reviewed: November 2026

On this page
  1. Overview
  2. What you get
  3. Who provides what
  4. Why Protofire
  5. Withdrawal checks
  6. EU rules
  7. Travel Rule routes
  8. Not the right fit
  9. How work starts
  10. Related guides and services
  11. FAQ

Work shipped for 60+ networks and 95+ protocols, including

  • Chainlink
  • Ethereum
  • Solana
  • Safe
  • Ripple
  • Aave

Why custody needs one compliance decision per transfer

In blockchain compliance integration, the decision belongs where compliance can still stop a crypto transfer. Compliance can stop a withdrawal before custody signs it and a deposit before the ledger credits it. For an issuer, compliance can also stop a transfer inside the token contract. After those points, the chain has already moved the value.

A firm that has chosen its KYC, screening and Travel Rule vendors still has to settle which answer custody waits for. When a withdrawal request arrives, each vendor answers in its own format. For example, Fireblocks lists three screening vendors side by side. Chainalysis returns a risk category, Elliptic returns a numeric score, and TRM Labs returns a category with an extra Wait outcome (Fireblocks). A category and a score need a mapping before they can be compared.

Since 30 December 2025, the EBA's sanctions-screening guidelines expect each crypto transfer to be screened before the assets reach the beneficiary (EBA/GL/2024/15, para 19). If nothing joins the vendors, each answer is stored in that vendor's own log. The firm then cannot show one decision per transfer or the rule version behind it.

Where the compliance decision is made in a crypto transfer

Vendors answer, and the decision service records one outcome per transfer.

The firm

Custody and ledger

Custody signs a withdrawal under the firm's own policies, and the ledger credits a deposit after the decision returns go.

Token contract

For an issuer, identity and transfer rules run inside the token, under keys the issuer holds.
Vendors and networks

KYC and screening vendors

The vendors return customer status, address risk and name hits, each in its own format.

Travel Rule route

A network or protocol transmits originator and beneficiary data for each transfer.
Protofire builds

Counterparty check

The check tells a provider from a self-hosted wallet using analytics, Travel Rule identifiers and ESMA's register.

Decision service

The service returns go, review or stop for each transfer, under rules that compliance signs, on credentials the firm holds.

Evidence store

The store keeps raw vendor answers, rule versions, decisions and reviewers.

What blockchain compliance integration gives the firm

A written rule set for go, review or stop

Protofire writes the rule set that turns four vendor answers into go, review or stop. The four are KYC status, the Travel Rule result, address risk and name hits. Each vendor timeout also gets a written rule. On Fireblocks, your administrators set a custody policy that accepts withdrawals only from the decision service's API user (Fireblocks).

A review opens a case with the evidence attached

Protofire hands each review to the case manager that your analysts already use. The analyst then decides with the vendor answers in front of them.

Rescreening after each sanctions-list change

A lapsed identity or a new sanctions hit stops the customer's next crypto withdrawal. After each list change, Protofire rescreens the customer base. We also re-run withdrawals already in the queue against the new list.

Different duties for provider and self-hosted addresses

A transfer to a provider and a transfer to a self-hosted wallet come with different duties. Protofire classifies each destination and matches EU providers against ESMA's register. We also collect ownership proofs where the law asks for them, and we rescreen the whitelist.

Holds, returns and freezes booked in the ledger

A deposit under review is kept in a finance-approved hold. Protofire books returns to the originator for transfers that lack data. We book freezes for confirmed sanctions matches. The firm pays the gas for a return, and that gas is booked as the firm's cost. For an issuer, we add transfer and freeze rules inside the token through ERC-3643 development.

Records that remain readable after a vendor change

The evidence store that Protofire builds keeps raw vendor answers, rule versions, decisions and reviewers. The store also keeps a written list of what each vendor can and cannot detect. A vendor change leaves the history readable. After launch, Protofire can watch vendor timeouts and unanswered Travel Rule messages under a written scope, as part of managed onchain operations.

What you buy from vendors and what Protofire builds

A firm can buy identity checks, risk data and Travel Rule messaging from vendors.The decision that joins them is built firm by firm.

Identity

Bought from a vendor: KYC and KYB checks, including unhosted wallet verification at some vendors

Protofire builds: A customer status that the transfer service reads, refreshed when a sanctions list changes

Address and transfer risk

Bought from a vendor: Results from Chainalysis, Elliptic or TRM Labs, each in a different format

Protofire builds: One severity scale that compliance signs, with each raw answer stored next to the decision

Travel Rule messaging

Bought from a vendor: Protocols and networks such as TRP, GTR and TRISA

Protofire builds: Counterparty classification, the send and receive steps, and a count of counterparties that fail to send data

Evidence

Bought from a vendor: Each vendor's own logs

Protofire builds: One record per transfer, with the vendor answers beside it

Our record: the Swarm Markets DEX core, built in 2021

In 2021 Protofire built the DEX core and subgraph for Swarm Markets.Swarm Markets was a BaFin-licensed DEX at launch, and only KYC-verified wallets trade on it. We also contributed to its dOTC contracts. Both repositories are public.

Swarm held the licenses and ran KYC itself. The Swarm Markets work applies to compliance integration because it was engineering for a venue whose operator holds the license and runs KYC. Protofire integrates Chainalysis, Elliptic, TRM Labs, Notabene and Sumsub, and each integration has its own page.

The checks a withdrawal passes before custody signs it

A withdrawal reaches custody after one recorded decision covers its customer status, destination, screening results and Travel Rule data.A deposit goes through the receiving side of the same checks before it is credited.

  1. Step 1

    Customer status check

    The transfer service reads the customer's KYC result and last sanctions screen. A stale status stops the withdrawal.
  2. Step 2

    Destination check: provider or self-hosted wallet

    Blockchain analytics, Travel Rule identifiers or the customer's own answer show whether the address belongs to a provider or is self-hosted (EBA/GL/2024/11, paras 77-78). Protofire matches an EU provider against ESMA's interim register (ESMA).
  3. Step 3

    Ownership proof for a self-hosted wallet

    For a self-hosted address above 1,000 euros, the provider must assess whether the customer owns it (Regulation (EU) 2023/1113, Art. 14(5)). The EBA accepts a signed message, a test amount or a remote onboarding check (para 83). For a Safe or another contract wallet, Protofire verifies the signature through EIP-1271 on the chain the transfer uses.
  4. Step 4

    Address and name screening

    The analytics vendor scores the destination address. The decision service then maps the answer onto your severity scale. Names go through fuzzy matching, which is tuned and documented for the supervisor (EBA/GL/2024/15, paras 24-25). Addresses go through exact matching plus analytics, and for EVM chains they are lowercased first.
  5. Step 5

    Travel Rule data sent through the chosen route

    Originator and beneficiary data is sent through the chosen route no later than the broadcast of the transaction (EBA/GL/2024/11, para 25). If no route reaches the counterparty, your written policy decides whether the withdrawal waits or stops.
  6. Step 6

    One recorded decision for each withdrawal

    The record holds the outcome (go, review or stop), each vendor answer, the rule version and the reviewers. On Fireblocks, Protofire writes an API Co-Signer callback that checks the decision's ID, destination and amount. In that callback, "one rejection denies the request" (Fireblocks). A review is settled before submission, because a rejected signing request fails for good.

The EU rules this build follows, with their dates

Travel Rule
The Travel Rule has applied since 30 December 2024, and it sets no minimum amount between providers (Regulation (EU) 2023/1113, recitals 27 and 30). The sender may not start a transfer before its duties are met (Art. 14(8)).
Missing data
When data is missing, the receiving provider executes, rejects, returns or suspends the transfer (Art. 17(1)). A counterparty that keeps failing is warned, then rejected or restricted, and reported (Art. 17(2)).
Sanctions screening
Since 30 December 2025, screened data is updated immediately after a new restrictive measure enters into force. The customer base is rescreened on each change (EBA/GL/2024/15, paras 9 and 16) (EBA).
Records
Records are kept for five years (Art. 26).
AML Regulation
From 10 July 2027, due diligence applies to occasional crypto transactions from 1,000 euros. Below that amount, identity checks with verification apply. Anonymous crypto-asset accounts are not allowed (Art. 19(3), 79) (Regulation (EU) 2024/1624).

Checked November 2026 against the EUR-Lex texts and the EBA's guidelines.

Choosing a Travel Rule route before the build

The Travel Rule route is chosen before the build, and the route sets which counterparties you can reach.Routes differ in who they reach, and a firm usually needs more than one. On one Fireblocks workspace, Notabene cannot run alongside Sumsub or GTR (Fireblocks). TRISA and TRP have been interoperable since 2023. Both are now under the OpenVASP Association, and TRISA has been under it since 1 October 2026 (OpenVASP). Protofire's EU Travel Rule guide scores eight routes on reach and data security.

For transfers of crypto-assets, several messaging [...] systems exist [...]. Not all are interoperable, which means that CASPs might have to use multiple systems to be able to transact with their counterparties. This can create data integration issues and hamper institutions' ability to comply with travel rule requirements.
European Banking Authority (EBA), Final report on guidelines, EU banking authority · EBA/GL/2024/11 on the Travel Rule, background section 3.1, 4 July 2024

When a separate compliance integration is not the right fit

A separate integration fits poorly when one platform already covers your flow, or when you need a compliance function rather than engineering.

  • You want a compliance opinion, filed reports or an outsourced officer. Protofire gives no legal or compliance opinion and files no reports. Protofire is not your compliance officer either. Your officers decide: they set thresholds, clear sanctions hits and file. We run no Travel Rule network and keep no screening database.
  • One platform and one vendor per job already cover your flow. Fireblocks checks transactions against your Travel Rule policy with Notabene, Sumsub or GTR (Fireblocks). For screening, Fireblocks connects Chainalysis, Elliptic or TRM Labs (Fireblocks). Fireblocks policies may be enough until a held amount needs a ledger entry.

How work with Protofire starts

You tell us the compliance vendors you contract today, your custody platform and the system that credits customer balances.From that list, Protofire lists each vendor answer that the decision service must read at each of your control points. The decision service runs in your infrastructure. Your staff hold its credentials, and no Protofire operator holds them. You own the evidence store.

Proposal
In writing, one business day after the discovery call: findings, a plan in phases and the first step we recommend.
Price
Fixed per phase when you commission it, against written acceptance criteria. Overruns inside them are ours to absorb, invoices follow delivered milestones, and you can stop at any phase boundary. Anything we operate after launch is priced in the proposal as its own recurring line, with the notice to end it.
Ownership
Code we write for you, contracts, the keys and credentials this work creates and the accounts your infrastructure runs in are yours by contract, within the license of any third-party software involved. Keys that a custody platform or a staking provider holds under its own key model stay with it under your contract; every other custody key stays with you or the custodian you appoint. Where the scope places something on servers we rent, it says what moves to you and when. An NDA is available from your first message, and we sign a data processing agreement (DPA) together with it.
After launch
Delivery closes with a hypercare window and a defect warranty, with their terms written into the proposal. A service we operate continues under its written scope until that scope ends.
Access
Read-only by default. A role that can start requests only if your written scope names one; never a signer, approver, administrator, key holder or recovery role on your contracts, wallets or custody platform. Services we build call each platform on credentials your staff issue and keep in your vault. Anything that approves or moves funds runs in your environment, and a scope under which we operate a service lists every write call it makes. Where the scope has us operate nodes, validators, monitors, explorers or indexers, it names the role and any key we hold on those servers, and in your own cloud account you can remove it.
Licenses
Protofire is an engineering firm and holds no financial or crypto-asset license; licensed activity stays with you and your providers.

How we work shows a worked proposal.

FAQ

What is blockchain compliance integration?
Blockchain compliance integration is the software that joins a firm's compliance vendors into one recorded decision for each crypto transfer. The vendors cover KYC, transaction screening, sanctions screening and the Travel Rule. The decision runs before custody signs a withdrawal and before the ledger credits a deposit. Protofire builds the integration between the vendors that the firm has chosen. The firm's compliance officers sign the rules.
Who can build the integration between our custody platform and our compliance vendors?
Protofire builds the integration between a firm's custody platform and its compliance vendors. Protofire's part is the decision service, the counterparty checks and the evidence store between the vendors you contract. We integrate Chainalysis, Elliptic, TRM Labs, Notabene and Sumsub. Your compliance officers sign the rule set before it goes live.
Does the EU Travel Rule apply to transfers under 1,000 euros?
Yes. Between providers, the EU Travel Rule sets no minimum amount. Crypto transfers face "the same requirements regardless of their amount" (recital 30). The 1,000-euro figure triggers a different duty, which is checking that a customer owns or controls a self-hosted address.
Can a smart contract still check sanctions onchain?
Yes, a smart contract can still check sanctions onchain for a token the firm controls. Before each transfer, an ERC-3643 token calls isVerified on the identity registry and canTransfer on the compliance contract (EIP-3643). Chainalysis no longer maintains its Sanctions Oracle, and the oracle's list has not changed since 18 March 2026 (Chainalysis). Chainlink ACE is in private beta. Its Active Monitoring, added on 7 October 2026, screens addresses you choose with TRM and acts on tokens you already run (release notes). For a token you do not control, the checks happen at signing and crediting.
How does a firm tell a provider's wallet from a self-hosted one?
A firm tells a provider's wallet from a self-hosted one by technical means first. The EBA names blockchain analytics, third-party data and messaging-system identifiers, and it falls back to asking the customer. The sender decides before the transfer starts, and the receiver decides before it credits the funds (EBA/GL/2024/11, para 79).
What changes for crypto KYC when the AML Regulation applies on 10 July 2027?
Two things change beyond the 1,000-euro due-diligence threshold and the ban on anonymous crypto-asset accounts. First, due diligence checks whether sanctioned persons control a corporate customer or own more than 50% of it (Art. 20(1)(d)). Second, AMLA's final draft standards of 30 September 2026 add screening of wallet addresses that appear on sanctions lists (AMLA). Those draft standards still await Commission adoption.
Can one vendor cover KYC, transaction screening and the Travel Rule?
For a small book, yes. Sumsub's crypto platform lists KYC, KYB, AML transaction monitoring, unhosted wallet verification and the Travel Rule (Sumsub). Larger firms often add a second analytics vendor, and two vendors mean two answer formats. Protofire's decision service stores the mapping between the two formats, which compliance signs. The service also keeps the raw vendor answers.

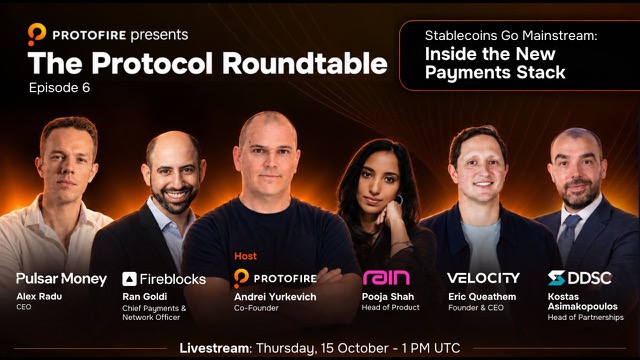
Discussed on The Protocol Roundtable

All episodes

Get a proposal

Tell us what you are building. An engineer reads it, we have a short call, and the written proposal follows within one business day.

Luis MedeirosField CTO, reads every request · LinkedIn

A demo or repository link also works.