RPC Node Hosting for Full and Archive Nodes on Your Own Domain
Protofire hosts full and archive nodes behind one dedicated RPC endpoint on your own domain, for chains, protocols and custodians. Under a written scope, we run the nodes and write down method limits and failover. Filecoin's newsletter thanked us for running Glif Nodes RPC, which we built.
Reviewed by Arsenii Petrovich, Offer Owner at ProtofireLast reviewed: November 2026
On this page
Work shipped for 60+ networks and 95+ protocols, including




RPC node hosting on a domain in your DNS zone
Each RPC plan sets its own eth_getLogs block cap, so code that works on one provider can fail on the next. For example, your indexer's backfill ran clean against one provider, and on the next it returns an error. Your wallet, your backend and your oracle nodes all hold the vendor's URL, so changing provider means a release in each of them.
With RPC node hosting, Protofire runs the endpoint and the full and archive nodes behind it, on a domain in your DNS zone. We write the limit per method, the history each consumer reads and the failover rule into the scope. Replacing an operator then becomes a DNS change.
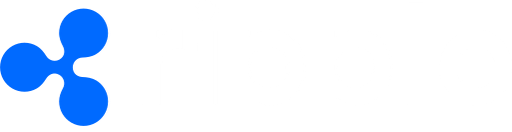
Who owns each hop of one RPC request
You keep the domain, the configs and the snapshots. Protofire runs the gateway, the router and the nodes under the scope.
Consumers
Domain and TLS
Snapshots
Gateway
Router
Client pool
Monitoring
Our record: Glif Nodes, the public Filecoin RPC service
Protofire built Glif Nodes, a public RPC service for Filecoin, and we run it.The records below are the evidence.
- Filecoin's own pagesFilecoin's newsletter of 29 May 2024 reported an average of 3 billion RPC requests a month on Glif Nodes. The newsletter recorded the service's top place in the Fil-RetroPGF round and thanked "the Protofire team for running Glif Nodes RPC". Filecoin's mainnet documentation lists Glif Nodes among its RPC providers. Protofire's Filecoin case study covers the build.
- LotusProtofire engineers contributed gateway methods to Lotus, the Filecoin reference node. The merged pull requests show this, and the earliest dates from March 2023. Protofire also publishes Lotus gateway builds and an Ethereum-RPC gateway for the Glif nodes on its GitHub.
- Tooling and archiveFrom 2020 to 2022 Protofire wrote open-source Filecoin node tooling, including a caching RPC proxy. In June 2023 we published how we handled a 37 TB Filecoin archive.
What RPC node hosting on your domain gives you
A change of operator is a DNS change
Wallets, backends and oracle nodes call a URL on your domain. So none of them needs a wallet or SDK update when the operator changes. Protofire serves the CNAME target and terminates TLS at the gateway. When we exit, we revoke the certificate for your hostname.
One published limit for each method
Your docs state one limit per method, and a caller that exceeds a limit gets an error that names the limit. Protofire sets API keys and a per-IP limit for public traffic. We also set block-span and response caps on eth_getLogs, and a lower class for wide logs and traces.
History as far back as your consumers read
You pay for the history depth your callers use, from a recent window to a full archive. Protofire sizes the node tier from your query mix and sends trace methods to the clients that serve them. A team that reads events alone can often skip archive, and indexing may serve that team better.
Failover on head number and block hash
A node that lags the group or is on another fork leaves rotation instead of answering. The router compares each node's head number and block hash with the group's. Protofire runs two execution clients behind the URL where the network has two, and we upgrade them one at a time.
Snapshots on storage you can read and a rehearsed restore
A successor operator starts from your copy, so it does not depend on the outgoing operator's goodwill. Snapshot jobs write to storage you can read, and a restore is rehearsed on a fresh node.
Figures in the agreement name their measurement point
A figure in the scope names its measurement point and the tool that reports it. The measurement point is the gateway, your consumers or a synthetic probe. Failures are counted by method class. A span rejected for exceeding the published limit counts as correct behavior, but a timeout inside the limit counts against the target.
How Protofire sets up and runs your RPC endpoint
- Step 1
Readiness review of your traffic
Protofire reads the methods your callers use and the history each caller needs. We also check which clients are available on the network and which parent-chain dependencies it has. The output is a written plan that names the node types and the clients. The plan also names the method limits and the hosting account. - Step 2
Config review before the first node syncs
The plan fixes the client mix for each pool, the sync strategy and the rollout order for forks and releases. Helm charts, Terraform and client flags go to your repository as reviewed commits. - Step 3
Gateway and limits table go live
API keys, limits by method class and WebSocket handling go in front of the nodes at the gateway. The router starts to route on head lag and block hash, and it routes trace methods. Your developers get the limits table to publish in your docs. - Step 4
Archive tier restored once before it is needed
Archive and trace nodes cover the history in the plan, and snapshot jobs write to storage you can read. A restore on a fresh node closes the step. - Step 5
DNS cutover once the new nodes are ready
The DNS record changes once the new nodes are synced and a certificate for your hostname is in place. The API keys must also be loaded at the gateway first. Consumers keep the same URL. - Step 6
On exit you keep the domain, the configs and the runbook
You own the domain, the deployment configs and the snapshots. The exit runbook lists the DNS change, the repositories and the snapshot location. It also lists the API keys and the credentials to revoke. If the nodes run in your own cloud account, you can remove Protofire's role. If the nodes run in a Protofire account, the scope lists what moves on exit: node data, snapshots and monitoring history.
How work with Protofire starts
To start, you send Protofire the network and your query mix per method.You also say how far back history must reach and where the endpoint domain is hosted. Protofire's first proposal fixes the hosting account, the on-call hours and the readiness review. The readiness review then sets the node types, clients and method limits. An EU financial entity records a hosted endpoint in its DORA register as ICT operation management (type S14 in Annex III to Implementing Regulation 2024/2956). The entity's risk team and counsel decide the entry. The full process is on how we work.
- Proposal
- In writing, one business day after the discovery call: findings, a plan in phases and the first step we recommend.
- Price
- Fixed per phase when you commission it, against written acceptance criteria. Overruns inside them are ours to absorb, invoices follow delivered milestones, and you can stop at any phase boundary. Anything we operate after launch is priced in the proposal as its own recurring line, with the notice to end it.
- Ownership
- Code we write for you, contracts, the keys and credentials this work creates and the accounts your infrastructure runs in are yours by contract, within the license of any third-party software involved. Keys that a custody platform or a staking provider holds under its own key model stay with it under your contract; every other custody key stays with you or the custodian you appoint. Where the scope places something on servers we rent, it says what moves to you and when. An NDA is available from your first message, and we sign a data processing agreement (DPA) together with it.
- After launch
- Delivery closes with a hypercare window and a defect warranty, with their terms written into the proposal. A service we operate continues under its written scope until that scope ends.
- Access
- Read-only by default. A role that can start requests only if your written scope names one; never a signer, approver, administrator, key holder or recovery role on your contracts, wallets or custody platform. Services we build call each platform on credentials your staff issue and keep in your vault. Anything that approves or moves funds runs in your environment, and a scope under which we operate a service lists every write call it makes. Where the scope has us operate nodes, validators, monitors, explorers or indexers, it names the role and any key we hold on those servers, and in your own cloud account you can remove it.
- Licenses
- Protofire is an engineering firm and holds no financial or crypto-asset license; licensed activity stays with you and your providers.
How we work shows a worked proposal.
When a hosted RPC endpoint from Protofire does not fit
- Your traffic is ordinary reads on a major chain. Alchemy's Pay As You Go plan has no eth_getLogs block-range cap on such a chain, and a shared provider is the better purchase.
- You need service credits for downtime from day one. With Protofire, service credits exist only if the scope creates them, so a vendor with a published SLA fits better.
- You need one node for a staging environment or a hackathon, or you need events alone. Self-hosting the node covers the first case, and indexing covers the second.
- You need block signing. Block signing involves keys and slashing, and our validator operations service covers it.
Related guides and services
Hosted RPC on Filecoin
Protofire built and runs the Glif public RPC endpoint and node infrastructure for Filecoin.
FAQ
What is RPC node hosting?
Who can host a dedicated RPC endpoint for our chain or protocol?
Do we need an archive node to read old events?
Do you commit to an uptime number?
What do Chainlink's RPC requirements ask of an endpoint?
How many clients should run behind one endpoint?
Do RPC nodes hold validator keys?
Get a proposal
Tell us what you are building. An engineer reads it, we have a short call, and the written proposal follows within one business day.