Tokenized Vault Infrastructure for Fund Issuers, Asset Managers and Fintechs
Protofire builds tokenized vault infrastructure as VaultOS: an ERC-4626/7540 vault core with separate controls. The fund issuer, asset manager or fintech that commissions it owns the contracts and roles. In 2021 Protofire built the DEX core for Swarm Markets, a BaFin-licensed DEX at launch where only KYC-verified wallets trade.
Reviewed by Luis Medeiros, Field CTO at ProtofireLast reviewed: November 2026
On this page
Work shipped for 60+ networks and 95+ protocols, including




Redemptions and keys in a tokenized fund's vault
Two choices decide how a tokenized fund's vault works: how it handles a redemption, and who holds the keys to the vault. For example, your tokenized fund has its first redemption requests. The vault that holds the shares settles a redemption in one transaction, up to a limit. The people who can change the vault's settings may not be you.
Protofire builds tokenized vault infrastructure in which the redemption rules are written for your product and the keys are owned by your firm.
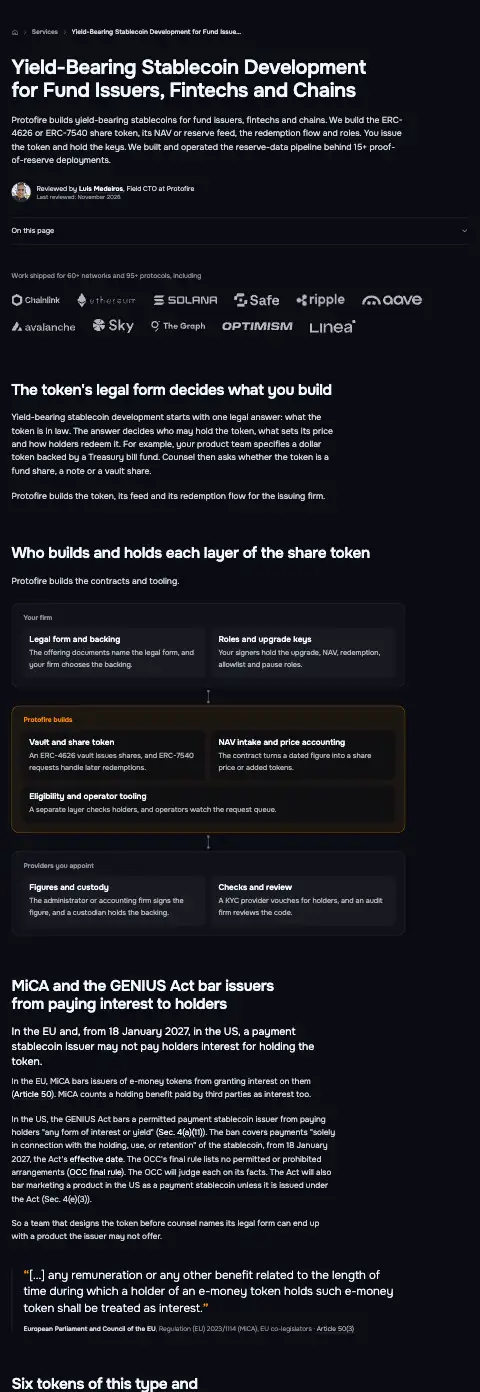
Layers of the vault and who builds, owns or supplies them
Protofire builds the vault and its controls. Your firm owns the contracts and decides who holds each role. Providers you appoint supply prices, investor checks and custody.
Vault core
Eligibility rules and roles
Operator tooling
Contracts, roles and upgrade keys
Strategy and operation
Share price and investor checks
Custody and audit
ERC-7540 redemption requests and who controls the vault
The choice of vault standard decides whether a redemption settles at once or as a request.ERC-4626, the base standard for tokenized vaults, covers a deposit and a withdrawal that settle at once, up to a limit. A fund that strikes a price once a day, or waits on an administrator, needs a different flow. ERC-7540, a Final standard that extends ERC-4626, lets an investor file a request that moves through Pending, Claimable and Claimed. ERC-7540 leaves the share price of a request "up to the Vault implementation", so the rule that sets that price is yours to write.
Who can change a vault depends on who holds its roles. In Morpho's Vault V2 documentation, a vault's Owner "can appoint the Curator and Sentinels", and the Curator "configures adapters, caps and fees" (Morpho Vault V2). When you deposit into a curated vault, those roles belong to the vault's owner and curator, and you hold none of them.
The tokenized market is now large enough for the choice of vault roles to matter. Pantera Capital's research team discussed its Q1 2026 State of Tokenization report in a call recorded on 24 June 2026. In that call the team described "593 tokenized assets across 11 asset classes representing $321bn in market value" (Pantera Capital). An issuer that puts its holders in someone else's curated vault accepts redemption rules and settings decided by that vault's owner and curator.
The standard is optimized for atomic deposits and redemptions up to a limit. If the limit is reached, no new deposits or redemptions can be submitted.
Tokenized vault infrastructure: what Protofire builds
Contracts, roles and upgrade keys your firm owns
Your organization holds the contracts, the roles and the upgrade keys, outside any shared protocol's governance. You assign each role. Protofire builds the vault and its controls so that each change goes through the roles you assign.
Subscriptions and redemptions as requests
Each subscription or redemption becomes a request that moves from Pending to Claimable to Claimed. That flow suits a fund that settles on a calendar. Protofire builds an ERC-4626 vault core with ERC-7540 request flows. We write with you the rule that gives a request its share price.
Eligibility checks after issuance
Protofire builds the vault to check who may hold shares and who may receive a transfer, at sign-up and after it. We write the eligibility and transfer rules into a layer separate from the vault core. We connect those rules to the KYC provider you choose.
Separate roles instead of one owner key
Protofire builds the vault so that one key does not hold the power to change settings, move capital and approve investors. You decide who holds each of those powers. The vault's code limits what each role can do. A Safe can serve as the signer set behind a role.
Operator tooling and a handover to your team
Protofire builds reporting and workflows for the operators who run the vault. The work includes written runbooks and a handover to your team. Where an onchain price source fits, the prices that requests settle at can come from our oracle integration work.
Our record: Swarm Markets, Safe and Solhint
Each of the three Protofire records below bears on one part of a vault: who may trade, who signs, and the tooling for the code.
Swarm Markets: the DEX core for a KYC-gated market
In 2021 Protofire built the DEX core (a Balancer fork) and subgraph for Swarm Markets and contributed to dOTC. Swarm Markets was a BaFin-licensed DEX at launch where only KYC-verified wallets trade. Swarm held the license and ran KYC and permissioning. A vault with eligibility rules faces the same two questions: who is allowed to hold, and who checks.
Safe, the multisig for a vault's signers
A Safe Ecosystem Foundation forum post of 27 May 2026 states that Protofire "has been contributing to Safe since 2018, touching the first versions of the codebase and helping expand Safe to over 100 chains". We deployed Safe on 120+ EVM networks, where it secures $2B+. Signers hold the roles of a vault you own, and Protofire's Safe multisig work covers the layer those signers use.
Solhint and Chainlink CCIP
Solhint, Protofire's open-source Solidity linter, has been downloaded 25M+ times from npm. The Ethereum Foundation's Ecosystem Support Program funded Protofire's work on Solhint in Q4 2022, Q4 2023 and Q1 2025. The Q1 2025 grant was for ongoing maintenance and support. Our Solhint page describes the linter. Protofire is a Chainlink core contributor and helps maintain Chainlink CCIP.
How a vault build with Protofire runs
You send what the vault will hold, the chains and who will manage the strategy.You also name the KYC provider and custodian you use, and the audit firm if you have picked one.
- Step 1
Scope: vault model, roles and providers
In the scope, Protofire settles whether the vault needs ERC-7540 request flows or a plain ERC-4626 core. We also settle who holds each role and which providers the vault connects to. You get a written architecture and deployment plan. - Step 2
Vault core and control hooks
Protofire builds the ERC-4626 core and the control hooks for the eligibility rules and roles. We also build the first integrations with your KYC provider and price source. - Step 3
Eligibility rules, roles and request flows
Protofire builds the eligibility and transfer rules and the role set you chose. We build the ERC-7540 request flows and the operator tooling in the same step. These four parts are tested together. - Step 4
Outside audit by the firm you pick
The code goes to the audit firm you pick. Protofire prepares the code, scopes the smart contract audit with you and responds to the findings. - Step 5
Limited pilot and handover
A pilot with limited capital runs first. After the pilot, the operational runbooks and the tooling pass to your team, which runs the vault. Alternatively, Protofire operates a part of the vault under a written scope that names the write calls the service makes.
How work with Protofire starts
A vault build begins with a written scope that fixes the vault model and the roles, and with the terms below.
- Proposal
- In writing, one business day after the discovery call: findings, a plan in phases and the first step we recommend.
- Price
- Fixed per phase when you commission it, against written acceptance criteria. Overruns inside them are ours to absorb, invoices follow delivered milestones, and you can stop at any phase boundary. Anything we operate after launch is priced in the proposal as its own recurring line, with the notice to end it.
- Ownership
- Code we write for you, contracts, the keys and credentials this work creates and the accounts your infrastructure runs in are yours by contract, within the license of any third-party software involved. Keys that a custody platform or a staking provider holds under its own key model stay with it under your contract; every other custody key stays with you or the custodian you appoint. Where the scope places something on servers we rent, it says what moves to you and when. An NDA is available from your first message, and we sign a data processing agreement (DPA) together with it.
- After launch
- Delivery closes with a hypercare window and a defect warranty, with their terms written into the proposal. A service we operate continues under its written scope until that scope ends.
- Access
- Read-only by default. A role that can start requests only if your written scope names one; never a signer, approver, administrator, key holder or recovery role on your contracts, wallets or custody platform. Services we build call each platform on credentials your staff issue and keep in your vault. Anything that approves or moves funds runs in your environment, and a scope under which we operate a service lists every write call it makes. Where the scope has us operate nodes, validators, monitors, explorers or indexers, it names the role and any key we hold on those servers, and in your own cloud account you can remove it.
- Licenses
- Protofire is an engineering firm and holds no financial or crypto-asset license; licensed activity stays with you and your providers.
How we work shows a worked proposal.
When a vault build with Protofire does not fit
In four cases, a deposit into someone else's vault, a plain vault or a shared protocol fits better than a build.
- You want to deposit into a vault that someone else curates. A deposit needs no build. Our lending against tokenized assets guide compares venues that take tokenized funds.
- You need one plain ERC-4626 vault, or request flows on a shared protocol's contracts. You accept its roles and rules. A factory deployment or that protocol will serve you.
- You want Protofire to manage the fund, run the vault or hold keys. Protofire holds no license and gives no legal opinion. After launch we take no administrator, signer or key-holder role on the vault. We hold no client funds or keys. Eligibility rules in a contract support your compliance. They do not replace your license, your KYC provider or your counsel.
- You need one permissioned token in depth and no vault around it. Our ERC-3643 development work covers that case.
Related guides and services
FAQ
What is tokenized vault infrastructure?
What is the difference between ERC-4626 and ERC-7540?
Who can build a branded vault for a fintech or an asset manager?
Should I deploy my own Morpho Vault V2 or build a vault?
Do shared protocols already support request-based redemption?
Who manages the strategy, and who operates the vault?
Does the build include an audit?
Get a proposal
Tell us what you are building. An engineer reads it, we have a short call, and the written proposal follows within one business day.